Cybersecurity as a key to success for logistics IT providers
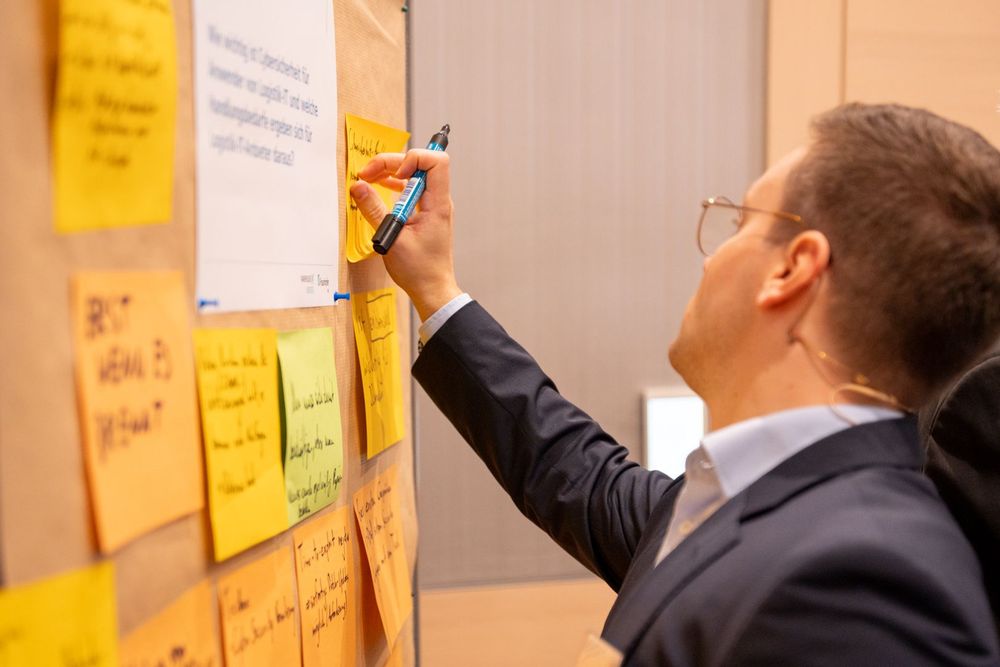
Cybersecurity is becoming a decisive factor for logistics IT providers. Customers increasingly assess security, driven by regulations, cyber-insurance requirements, and growing awareness of cyber risks. At the »warehouse logistics« participant meeting held on 9 September 2026 at the Westfalenhallen in Dortmund, logistics IT providers discussed current market developments in an interactive workshop format called Gallery Walk. The discussion centered on the following key question: How important is cybersecurity to the customers of logistics IT providers, and what conclusions do the providers draw from this for themselves? The following findings are an excerpt from this discussion.
© Vinzenz Neugebauer - Fraunhofer IML
Cybersecurity: Firmly on the customer agenda
Just how important cybersecurity is to customers depends heavily on the individual company. The spectrum ranges from the issue barely being discussed to extensive certification requirements. Yet the trend is clear: regardless of size or sector, the issue is gaining relevance across all industries. Whilst it has often been on the agenda at large companies for some time, smaller firms are increasingly catching up, not least because media coverage of cyberattacks is raising awareness of the risks. In tender processes, cybersecurity is increasingly the deciding factor in whether a supplier is shortlisted at all.
The point at which the issue arises during the course of a project has also shifted: many clients now raise the issue of cybersecurity even before awarding a contract, for example to check whether the provider’s operational concept aligns with their own requirements. At some providers, security engineers now regularly sit at the negotiating table, whilst at others the topic is firmly embedded in the onboarding process. In AI projects in particular, cybersecurity is a key talking point right from the start.
What is driving this trend?
Several factors are behind this growing importance. Regulatory requirements such as the NIS 2 Directive oblige many companies to implement more comprehensive security measures. Cyber insurance policies also require certain security standards to be met before cover is provided. Customers are increasingly passing on these requirements to their IT providers. Internal factors also play a role: companies with their own IT security departments prioritize the issue more highly, and specific incidents in their own environment often serve as a wake-up call. A particular dynamic arises when executives are held personally liable, as this immediately turns the topic into a management responsibility. Automated warehouse solutions are particularly at risk, as in an emergency, literally nothing can get in or out.
How providers are responding and where there are still issues
The increased sense of urgency is having an effect: many providers are relying on up-to-date backup plans, regular testing of their contingency plans and penetration tests to ensure they can react quickly in the event of an emergency. After all, time is working against them: the so-called Time-to-Exploit is now often negative, with attackers sometimes exploiting vulnerabilities even before a patch is available. Consequently, lifecycle management and rapid patching have long been part of the standard portfolio for many providers. Those who openly share their own experiences of security incidents and can demonstrate the lessons they have learnt from them come across as particularly credible.
However, this does not fully resolve the issue: service providers must remain able to operate on behalf of their clients even in the event of a crisis and are increasingly required to demonstrate that agreed security standards are actually being met. Adding to the challenge, the requirement documents in tenders are becoming increasingly extensive and individualized, as each customer brings their own templates and criteria to the table. Defining clear lines of responsibility between the client and the provider therefore remains an ongoing task.
One thing is certain: for logistics IT providers, cybersecurity is no longer merely an optional extra, but a core competence that runs through every level of their own systems and their collaboration with clients.
This insight is just an extract from the results of the Gallery Walk. The cybersecurity station was one of four stations in the interactive workshop. The full summary of all the results is available to download https://www.warehouse-logistics.com/en/publications/perspectives-on-logistics-it-results-of-the-gallery-walk-2026